

详细内容
🤍agent.security - Permit's New Platform for Enterprise-Grade AI Agent Security | Try it here🤍


End-to-end authorization platform anyone can use
A no-code authorization platformanyone can use.
-

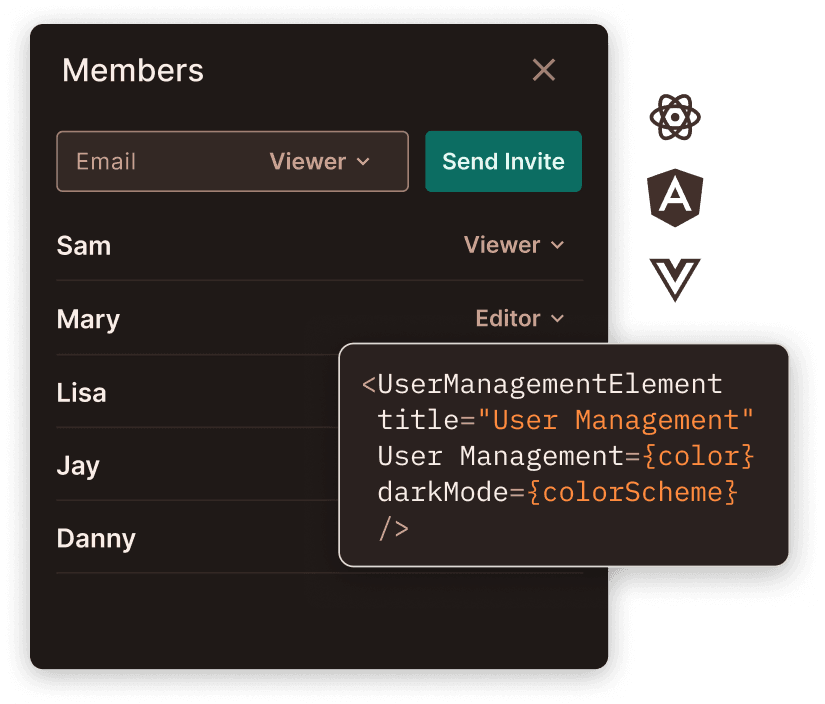
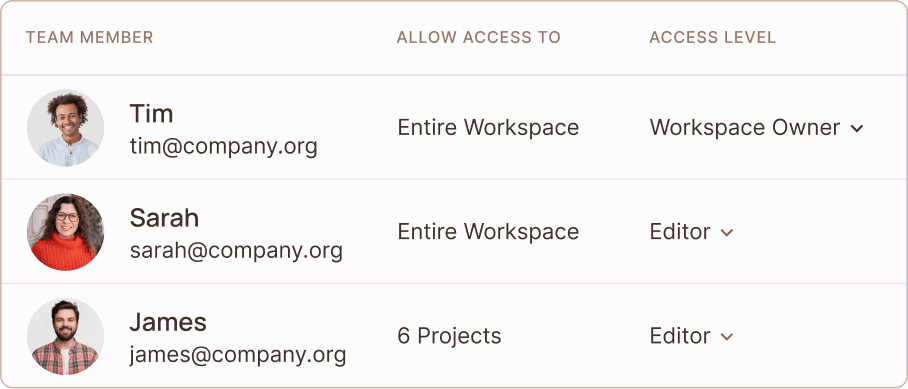
Allow your entire team - from devs to sales, to securely manage permissions -
The only solution with a no-code policy editor. Supports any model - RBAC, ABAC and ReBAC. -
Permit generates fully transparent policy as code based on OPA's Rego or AWS' Cedar -
Everything is managed as code in Git and controlled with a simple API
See how it works


Create RoleSync UserCreate ResourceCreate Permission


Permit CLI
Developer-First Integrated Authorization
Author, Automate, Test, and Deploy Authorization Policies Directly from the Command Line
npm i -g @permitio/cli
or
npm i -g @permitio/cli
or


RBAC
Role based access

default allow := false
allow if {
    some role in data.users[input.user].roles
    actions := roles[role][input.resource.type]
    input.action in actions
}
roles["Banker"]["Loan"] := [\
  	 "View","Approve","Decline"\
]
Policy UI Editor
Policy as Code
Create dynamic Role Based Access Control policies, like:
" Banker can Approve Loan"

ABAC
Granular attributes

default allow := false
allow if {
    some _, allowed_actions in conditions
    input.action in allowed_actions[input.resource.type]
}
conditions["Weekend Shift Employee"]["Database"] := [\
  	 "Read", "Update", "Backup", "Restore"\
] if {
  	 work_days := { day |
      day := data.users[input.user].attributes.work_days[_]
    }
    count({"Saturday", "Sunday"} & work_days) > 0
}
Policy UI Editor
Policy as Code
Build nuanced attribute based access control policies by adding attributes, like:
" Weekend Shift Employees
can access Database during Weekend "
ReBAC
Resource and user hierarchies

default allow := false
allow if {
  	 patient_caregiver = true
}
patient_caregiver if {
  	 user_roles := data.users[input.user].roles
  	 some assigned_resource, assigned_roles in user_roles
    some role in assigned_roles
    input.action in roles[role][input.resource.type]
    assigned_resource in resource_relationships
}
resource_relationships[resource] {
    related_resources := graph.reachable(
      full_graph,{input.resource.id}
    )
    some resource in related_resources
}
full_graph[child] := parent if {
  	 all_resources := [resource | resource := data.resources[_]]
   	some child, parent_resource in object.union_n(all_resources)
  	 parent := [object.get(parent_resource, "parent_id", null)]
}
roles["Caregiver"]["Record"] := ["View", "Update", "Share", "Archive"]
Policy UI Editor
Policy as Code
Create policies based on relationships between users and resources, like:
" Caregiver of a Patient
can View Patient's Medical Files "
default allow := false
allow if {
  some role in data.users[input.user].roles
  actions := roles[role][input.resource.type]
  input.action in actions
}
roles["Banker"]["Loan"] := [\
	 "View","Approve","Decline"\
]
default allow := false
allow if {
  some _, allowed_actions in conditions
  input.action in allowed_actions[input.resource.type]
}
conditions["Weekend Shift Employee"]["Database"] := [\
	 "Read", "Update", "Backup", "Restore"\
] if {
	 work_days := { day |
    day := data.users[input.user].attributes.work_days[_]
  }
  count({"Saturday", "Sunday"} & work_days) > 0
}

default allow := false
allow if {
	 patient_caregiver = true
}
patient_caregiver if {
	 user_roles := data.users[input.user].roles
	 some assigned_resource, assigned_roles in user_roles
  some role in assigned_roles
  input.action in roles[role][input.resource.type]
  assigned_resource in resource_relationships
}
resource_relationships[resource] {
  related_resources := graph.reachable(
    full_graph,{input.resource.id}
  )
  some resource in related_resources
}
full_graph[child] := parent if {
	 all_resources := [resource | resource := data.resources[_]]
 	some child, parent_resource in object.union_n(all_resources)
	 parent := [object.get(parent_resource, "parent_id", null)]
}
roles["Caregiver"]["Record"] := ["View", "Update", "Share", "Archive"]
Policy UI Editor
Policy as Code
 RBAC Role based access
Create dynamic Role Based Access Control policies, like:
" Banker can Approve Loan"
 ABAC Granular attributes
 ReBAC Resource/User hierarchies
Policy UI Editor
Policy as Code
Homebrew
Use setting
With Permit
NodeJS
Python
Golang
Java
C#
React
Gateway
Kong
Ruby
-

Seamlessly migrate from any existing authorization solution -
GitOps and Multi-tenancy
available out-of-the-box
Secure, event-driven, compliant.
Engines


OPA / Cedar
Policy Updater

OPAL
-
All authorization decisions are made on your side with zero latency
-
Use sensitive data for authorization decisions, without it ever leaving your VPC/Network
-
Permit is always up (+99.99) - but you are not dependent on our availability
-
Compliant with HIPAA, SOC2, and more
Engines
OPA / Cedar
Policy Updater
OPAL
How the Hybrid Model fits your architecture?
 Talk with Our Devs






 \
 \
 \

 \
 \
 \
 \
 \

 \
 \
Got questions? Talk with our devs.
Just listen to what these folks had to say...
Tal Saiag
Granulate Founder & CTO
At Granulate we optimize our customers’ most critical systems; as a result, getting access control right is of the highest importance. Full stack permissions as a service allows our developers to focus on their core product. I was extremely impressed both by Permit.io’s technology and its dedication to customer service.
Matan Bakshi
Buzzer.ai Founder & CTO
Building authorization for Buzzer’s call-rep on-demand service was a challenging task, but with Permit.io we were able to get it up and running end-to-end in just a few days.
Ran Ribenzaft
Cisco, Epsagon CTO
At Epsagon (acquired by Cisco) we are no strangers to the complexity of microservices. Access control demands of microservices are never-ending , so they require a modern stack that can quickly adapt to the most demanding tech and security needs.
Nate Young
CIO, Maricopa County Recorder's Office
Permit’s intuitive policy editor allows access to complex attribute-based conditions that are robust enough for our developers to use, yet simple enough for our non-technical staff to configure without the need for IT assistance
Hongbo Miao
Tesla Senior Software Engineer
Moving to modern authorization for microservices is no easy feat, but OPAL made it easy. When I was learning and exploring replicator solutions for OPA myself in my free time, I found that OPAL is a very mature solution for the open-policy administration layer and beyond.
Jean Philippe Boul
Co-founder & COO Jules AI
At Jules we aim to streamline the process of buying/selling recycled materials, and sharing access as part of our portal is an important step to achieve that. Allowing users to share access is both important to get right and hard to do so, we're delighted to have Permit solve this problem for us end to end.
Our customers have many stories to tell, hear it from them!


Join our Community
2938 Members
 Join Permit's Slack